- Architecture selection — custodial, non-custodial, or MPC (multi-party computation) key model.
- Security design — key generation, encrypted storage, signing flow, and recovery logic.
- Multi-chain integration — node deployment and RPC access for every supported blockchain.
- Compliance layer — KYC/AML checks, transaction monitoring, and jurisdiction-specific rules.
- Production hardening — fee engine, withdrawal pipeline, monitoring, and release gates.
Custodial, Non-Custodial, or MPC: Choosing the Wallet's Key Model
Every Web3 wallet project starts with one decision that shapes everything downstream: who holds the private key. A custodial wallet architecture puts your platform in control of the key, which simplifies recovery and lets you offer fiat on-ramps easily, but it also makes your company a regulated custodian in most US states. A non-custodial wallet hands the key to the user through a seed phrase or hardware device, which removes custody risk from your business but pushes support costs up — a lost seed phrase means lost funds, period. MPC wallets split the key into encrypted shards distributed across multiple parties, so no single device or server ever holds the complete key, and that model has become the default choice for institutional and high-net-worth products in 2026.
| Model | Who Holds the Key | Regulatory Exposure | User Friction | Typical Buyer |
| Custodial | Platform | High (MSB/MTL licensing likely required) | Low | Exchanges, neobanks |
| Non-custodial (HD wallet) | User | Low | High (seed phrase management) | DeFi users, self-custody products |
| MPC / smart contract wallet | Distributed / on-chain logic | Medium | Medium (social recovery, gas abstraction) | Institutional trading, consumer fintech |
The technology decision affects the whole tech stack. Custodial and MPC wallets typically run on a microservice backend (Laravel or Node.js, PostgreSQL, Redis for session and cache layers) with a blockchain-node layer handling signing requests. Non-custodial wallets shift most of that logic to the client — mobile or browser extension — and the backend becomes a thin layer for price feeds, push notifications, and optional fiat rails.
Security Architecture: From Key Generation to Transaction Signing
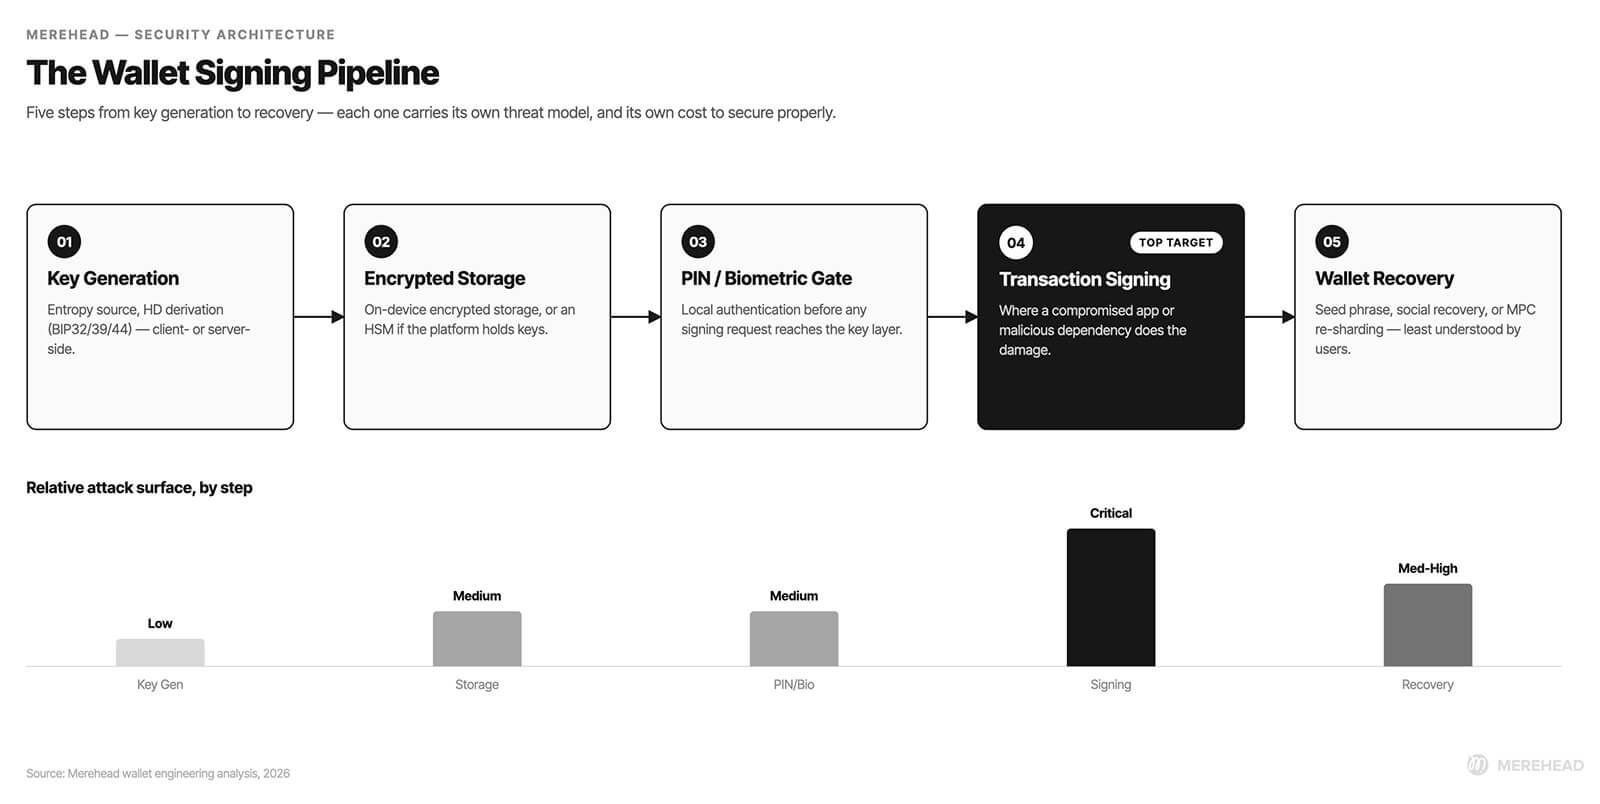
A wallet's security model isn't one feature — it's a pipeline, and every step needs its own threat model:
- Key generation: entropy source, HD derivation (BIP32/BIP39/BIP44), and whether generation happens client-side or server-side.
- Private key storage: encrypted local storage on-device, or an HSM (hardware security module) if the platform holds keys.
- PIN/biometric validation: local authentication gate before any signing request reaches the key layer.
- Transaction signing: the step attackers actually target — this is where a compromised app or a malicious dependency does the damage.
- Wallet recovery: seed phrase, social recovery, or MPC re-sharding — the flow users interact with the least and misunderstand the most.
Every commercial wallet estimate we scope treats these five steps as separate line items, because each one has a different attack surface and a different cost to secure properly.
We apply the same layered security thinking to wallet infrastructure that we use across our crypto exchange security architecture work — treating key management, transaction validation, and monitoring as independent systems rather than a single "security feature" bolted on at the end.
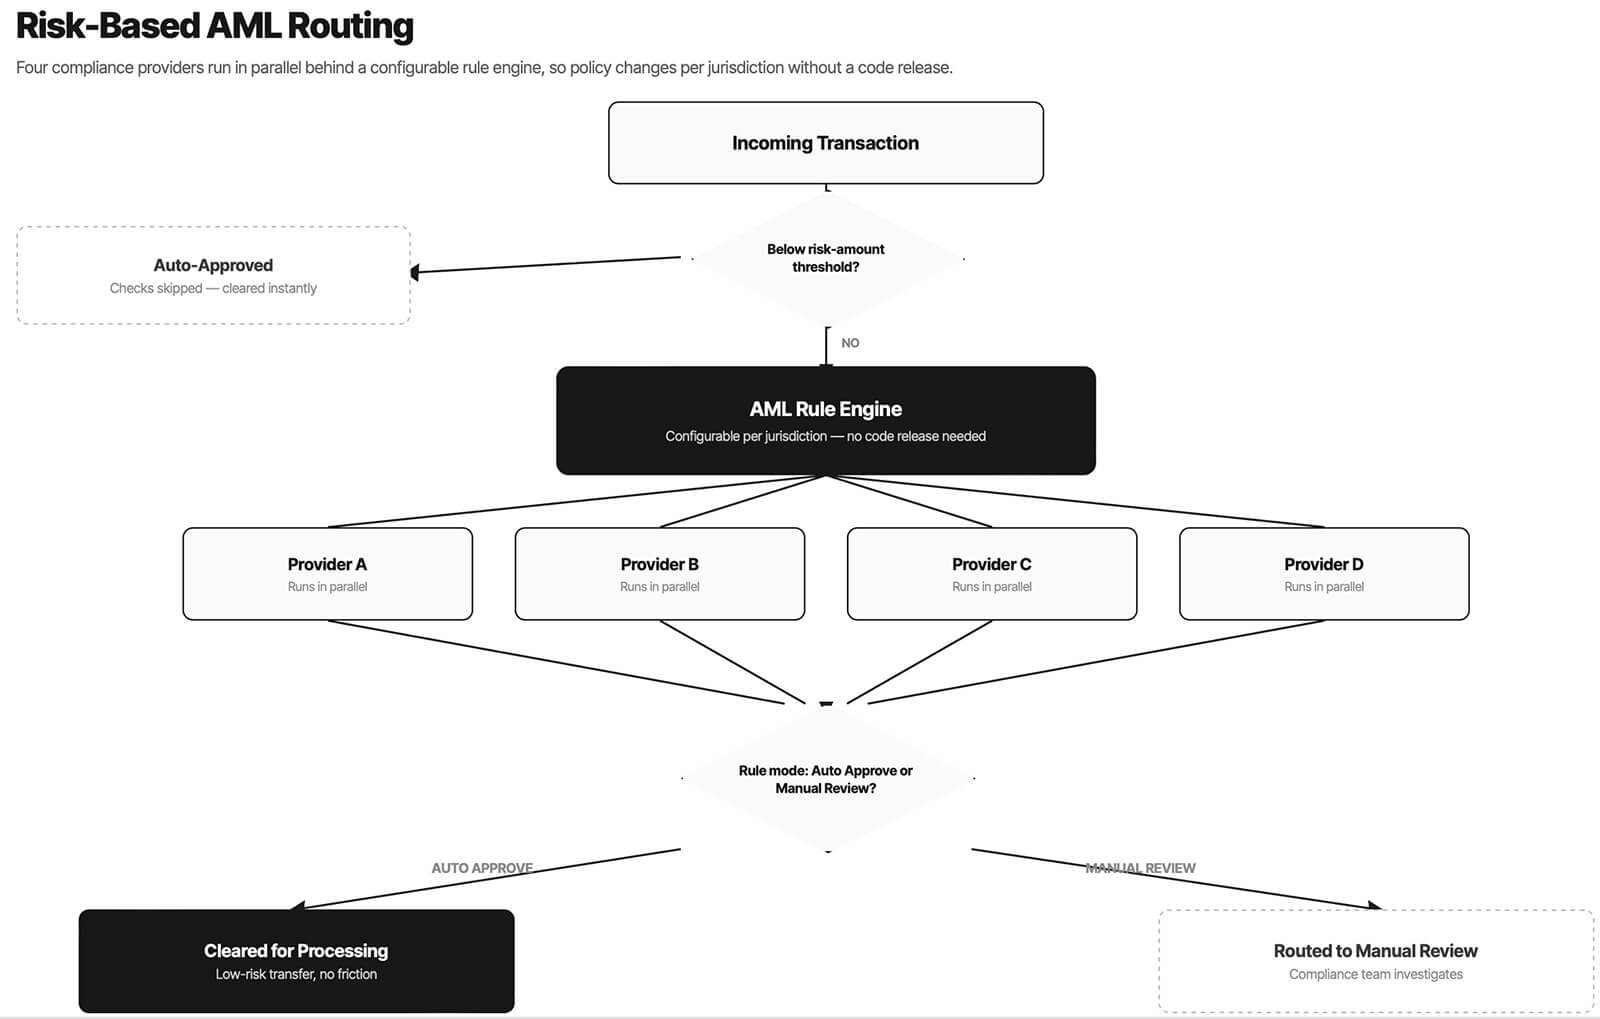
We built a configurable AML risk engine that runs four compliance providers in parallel, with rule modes ranging from Auto Approve to Manual Review, and a risk-amount threshold that skips checks on small transactions automatically. The compliance team tunes the policy per jurisdiction without a single code release.
 Yuri MusienkoBusiness developer, Merehead
That project came from a fintech platform where a single AML provider was both a bottleneck and a single point of failure: every policy change meant a developer ticket. We rebuilt it as a rule-based engine — four providers running in parallel, dynamic provider selection by configuration, and a "risk amount skip" parameter that lets low-value transactions clear instantly while high-risk ones route to manual review.
The same withdrawal flow got symmetrical logic, validated across nine test scenarios covering every combination of check mode and risk tier. The result: the compliance team now adjusts AML posture by market or risk profile without touching the codebase, and low-risk users stop feeling like they're under investigation for a $20 transfer.
Multi-Chain Infrastructure: What Node Deployment Actually Costs You
A wallet that only supports one chain is a demo, not a product. Supporting multiple chains means deploying and maintaining RPC nodes (or paying for managed node providers) for every network you list, and EVM chains behave very differently from UTXO chains like Bitcoin or account-based chains like Solana when it comes to transaction finality, fee estimation, and address formats.
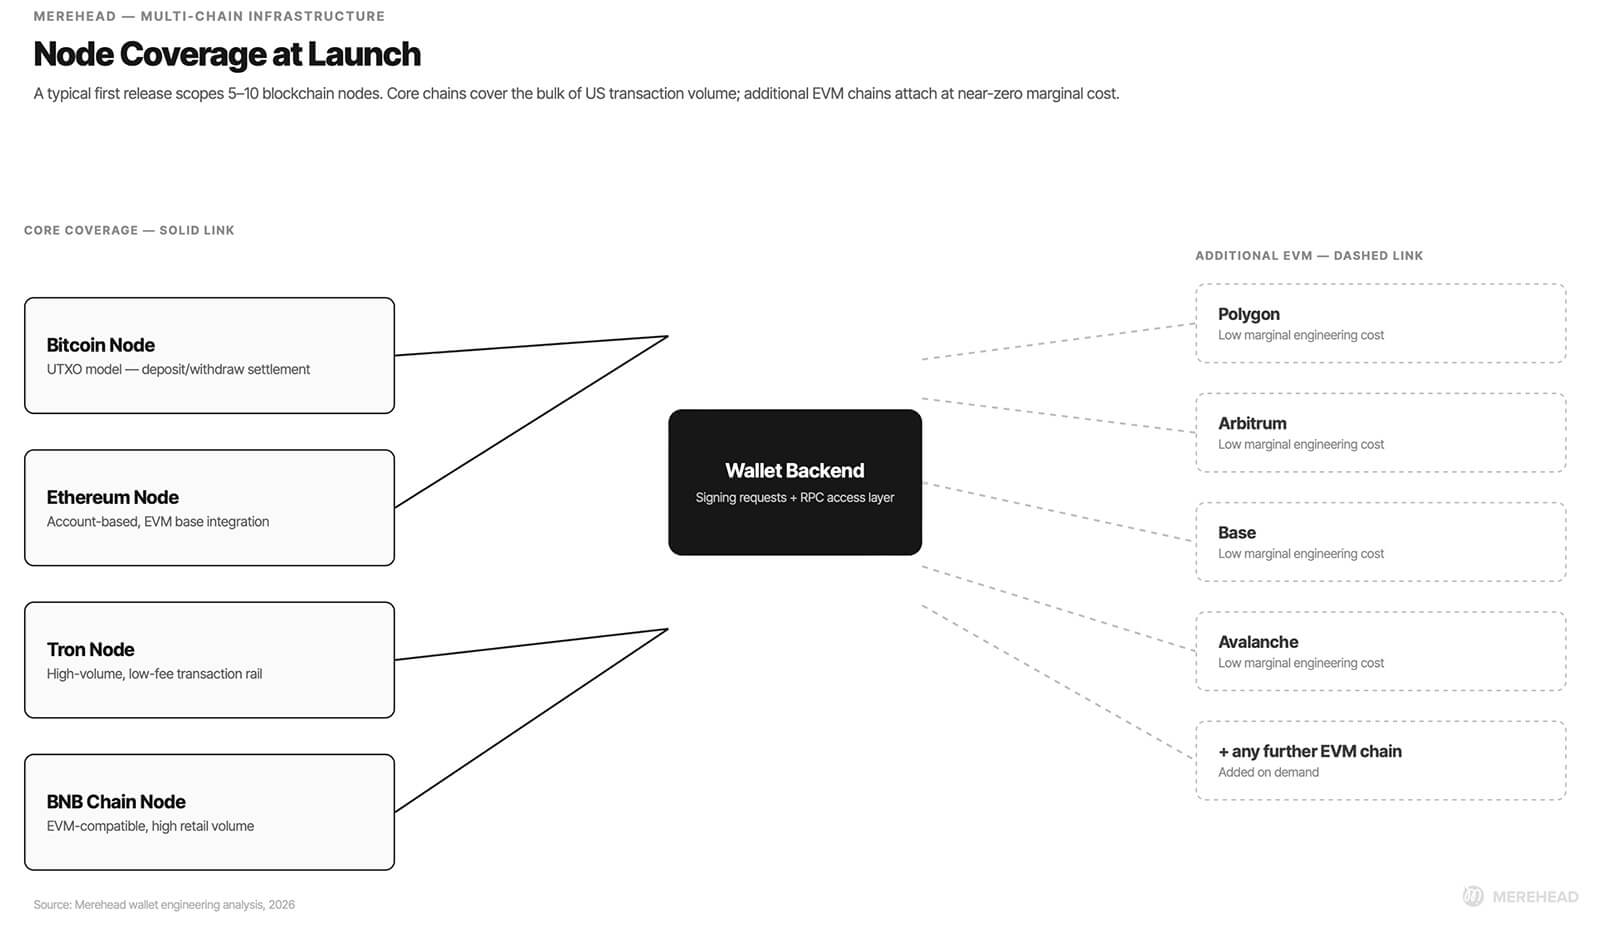
Our commercial offers for wallet projects typically scope 5 to 10 blockchain nodes for a first release — Bitcoin, Ethereum, Tron, and BNB Chain cover the bulk of real transaction volume for a US-facing product, with additional EVM-compatible chains added at near-zero marginal engineering cost once the base integration exists.
We deployed a production-ready withdrawal pipeline across Ethereum, Tron, and BNB Chain, with an AML filter gating every transaction and a structured release process — Ready for Prod, then Upload for Prod, with a hard pre-prod-to-prod parity check before anything ships.
Yuri MusienkoBusiness developer, MereheadThe withdrawal pipeline reached that state after we ran deposit-to-withdraw-to-auth end-to-end testing on the full user path, not just unit tests on individual modules — registration, authorization, deposit, and withdrawal chained together, because a wallet that passes isolated tests can still break at the seams between account state, node access, and backend services.
That's the difference between "the transaction went through in staging" and a system your compliance and support teams can actually run in production. We go deeper into how this kind of layered infrastructure gets designed for scale in our breakdown of crypto exchange architecture, since the same node-management and settlement logic underpins both wallets and trading platforms.
Dynamic Fee Engines and Why Static Withdrawal Fees Lose Money
Network fees move fast — a gas spike can turn a profitable withdrawal into a loss in the time it takes a user to click "confirm." A static fee schedule can't track that, so any wallet handling real volume needs a fee engine that reads live network cost and recalculates before the transaction settles.
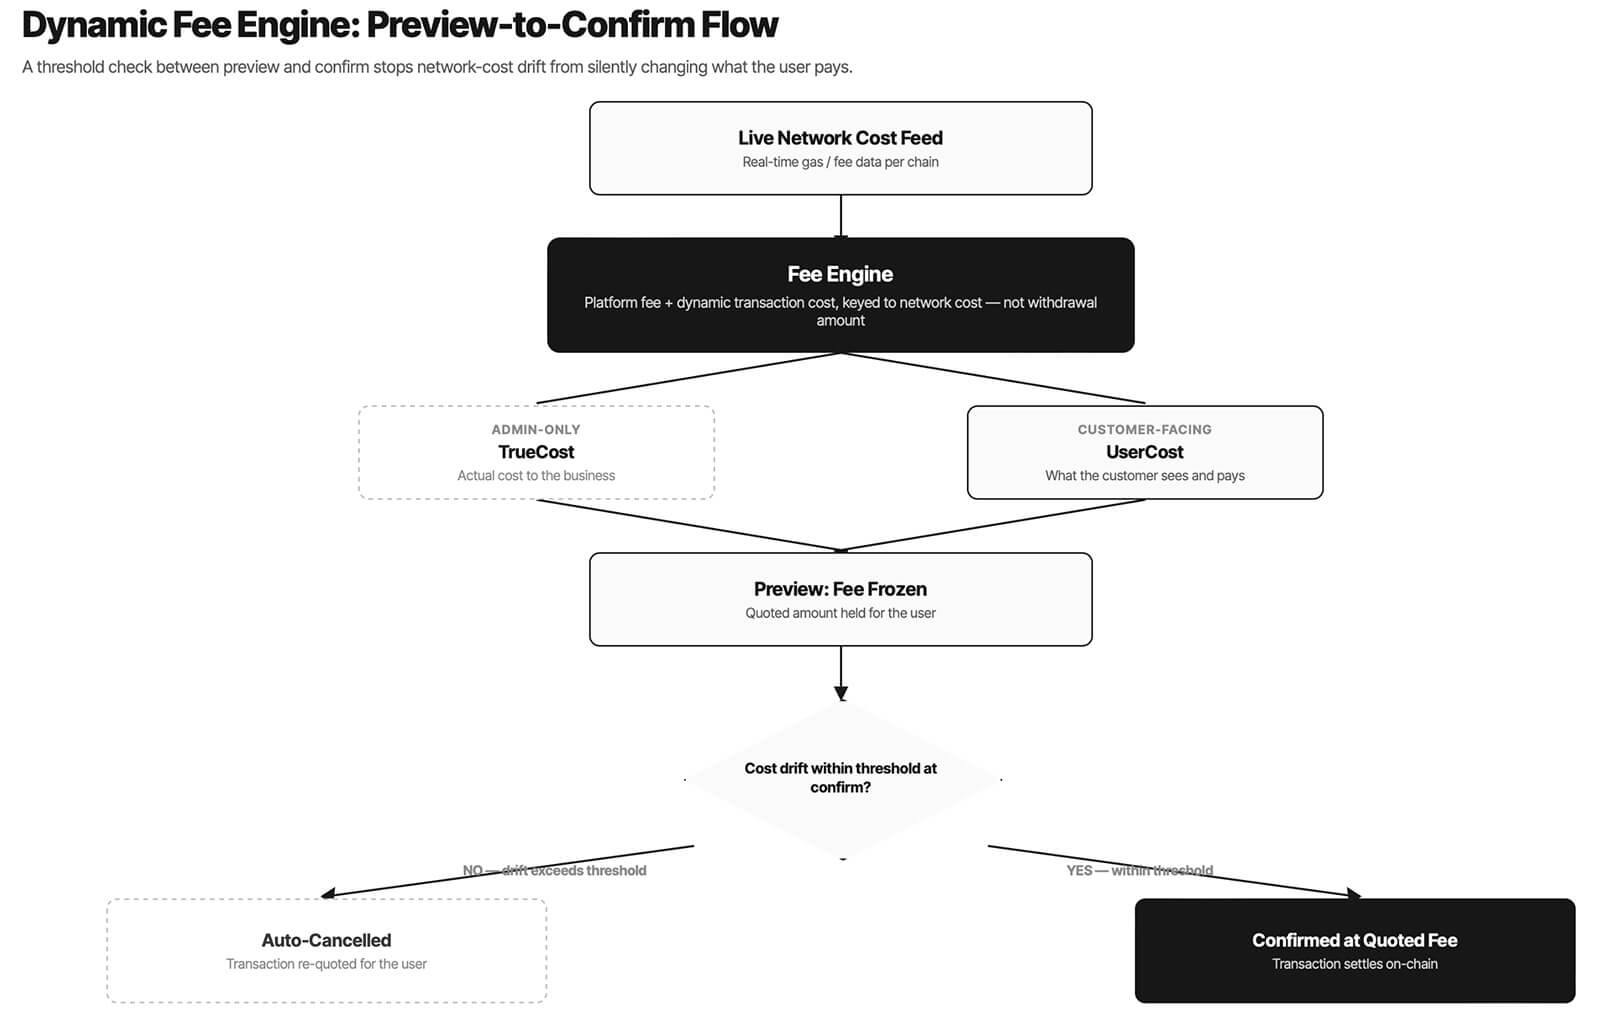
We built a hybrid fee model — a platform fee plus a dynamic transaction cost keyed to the blockchain-derived network cost, not the withdrawal amount — with threshold-based protection that freezes the fee at preview and automatically cancels the transaction if the recalculated cost drifts past a set threshold at confirm.
Yuri MusienkoBusiness developer, MereheadThat threshold check matters more than it sounds. Before it existed, a user could preview a fee, wait, confirm, and get charged a different amount because network cost moved in between — a classic source of support tickets and chargebacks. Now the platform separates "TrueCost" (what the transaction actually costs the business, visible only to admins) from "UserCost" (what the customer sees and pays), which gives finance a clean view of margin per transaction without exposing internal cost data to the front end. For a CTO, this single component is usually the difference between a wallet that operates at a stable margin and one that quietly bleeds money during volatile weeks.
Web3 Wallet Development Cost in 2026
Cost depends far more on architecture than on feature count. A minimal custodial wallet module and a full cold-storage hardware-integrated wallet can differ by $70,000+ for the same core promise — "store and move crypto securely."
| Wallet Type | Core Scope | Price Range | Timeline |
| Custodial wallet module (web app) | Deposit/withdraw, balances, transaction history | $25,000 – $43,000 | 1.5 – 2 months |
| Custodial wallet + exchange (backend + admin) | Wallet logic, 5–10 blockchain nodes, payment gateway, KYC | $28,000 – $36,000 | 2 – 3 months |
| Non-custodial wallet + exchange (backend + admin) | Hot wallet generation, 10–50 chains, optional NFT support | $40,000 – $74,000 | 2 – 3 months |
| Cold wallet software (web app) | Hardware device integration, key generation, 10 nodes, fiat on-ramp | $84,000 – $97,000 | 2 – 3 months |
| Cold wallet mobile app (iOS/Android, NFC signing) | Biometric auth, NFC transaction signing, fiat on-ramp | $119,000 | 2 – 3 months |
Mobile apps with NFC-based hardware signing sit at the top of the range mainly because of the security-testing overhead, not the UI work — every signing path through a physical device needs its own QA pass. If your roadmap includes both a web dashboard and native mobile apps, expect the two builds to run partly in parallel rather than sequentially, which is one of the biggest levers for compressing timeline without cutting scope. For a deeper walkthrough of how these cost drivers break down by feature, see our crypto wallet development cost guide.
Compliance: KYC/AML for a US-Facing Wallet
A wallet that touches fiat, or that lets users cash out to a bank account, puts your company inside the scope of US Money Services Business (MSB) rules and state-level Money Transmitter Licensing in most cases — non-custodial, pure crypto-to-crypto wallets carry a lighter compliance burden but aren't automatically exempt if you add any fiat rail later.
Build the compliance layer as a swappable module from day one, not a hardcoded integration with one KYC vendor: providers change pricing, coverage, and false-positive rates often enough that a hardcoded integration becomes technical debt within a year.
Every AML integration we've shipped that survived past year one was built as a rule-configurable layer, not a single vendor call baked into the transaction flow.
Yuri MusienkoBusiness developer, MereheadOur team's approach to this problem overlaps closely with what we've documented in blockchain-based KYC use cases — the same on-chain identity verification patterns that work for exchanges apply directly to wallets that need to onboard verified users without re-running full KYC for every product surface.
Smart Contract Wallets, Account Abstraction, and What's Actually New
ERC-4337 account abstraction changed what a "wallet" can be: instead of a single private key controlling an externally owned account, a smart contract wallet can enforce spending limits, support social recovery, sponsor gas fees for users, and batch multiple actions into one transaction. For a consumer product, this closes the single biggest onboarding gap in Web3 — users no longer need to buy native gas tokens before they can do anything. For an institutional product, programmable spending rules and multi-signature approval flows matter more than gas abstraction.
If you're evaluating whether to build on account abstraction now or wait, the honest answer is: build it if your users are non-crypto-native (gas abstraction removes real friction), and treat it as optional if your users already manage seed phrases comfortably.
One related pattern worth tracking rather than betting on: Ricardian-style contracts, which pair a human-readable legal agreement with the machine-executable smart contract logic. It solves a real dispute-resolution gap in on-chain agreements, but tooling and legal precedent for it are still early — worth a mention in your architecture docs, not a line item in your MVP scope. We cover the broader landscape of contract types and when each one applies in our guide to smart contract development.
Need to Launch Faster? A Ready-Made Alternative
Custom development gives you full control over architecture and compliance posture, but it isn't always the right starting point — if you need to validate demand before committing to a 2–3 month custom build, a white-label foundation with the core wallet, trading, and admin modules already built can get you to market in days instead of months, with custom modules layered in once the product proves itself.
FAQ
Cost ranges from roughly $25,000 for a custodial wallet module to $119,000 for a full cold-storage mobile wallet with hardware NFC signing. The main cost drivers are the key custody model, the number of blockchains supported, and whether the product includes a fiat on-ramp.
In a custodial wallet, the platform holds and manages the private key, which simplifies recovery but adds regulatory exposure. In a non-custodial wallet, the user holds the key through a seed phrase or hardware device, which removes custody risk from the business but shifts recovery responsibility entirely to the user.
MPC wallets split a single key into encrypted shards, so no complete key ever exists in one place, while multi-signature wallets use multiple separate keys and an on-chain approval threshold. MPC typically offers lower gas costs and works across any chain, while multi-sig is simpler to audit and has longer-established tooling.
Most commercial wallet launches scope 5 to 10 chains, typically Bitcoin, Ethereum, Tron, and BNB Chain, which cover the majority of real transaction volume. Additional EVM-compatible chains can usually be added at low marginal cost once the base multi-chain infrastructure exists.
A pure crypto-to-crypto non-custodial wallet carries a lighter compliance burden than a custodial one, but adding any fiat on-ramp, off-ramp, or bank integration typically brings the product under Money Services Business and state Money Transmitter Licensing requirements in the US.
Account abstraction lets a smart contract wallet enforce spending limits, support social recovery, and sponsor gas fees, removing the requirement for users to hold native gas tokens. It's most valuable for consumer products onboarding non-crypto-native users, and less critical for institutional users who already manage seed phrases and multi-sig flows.